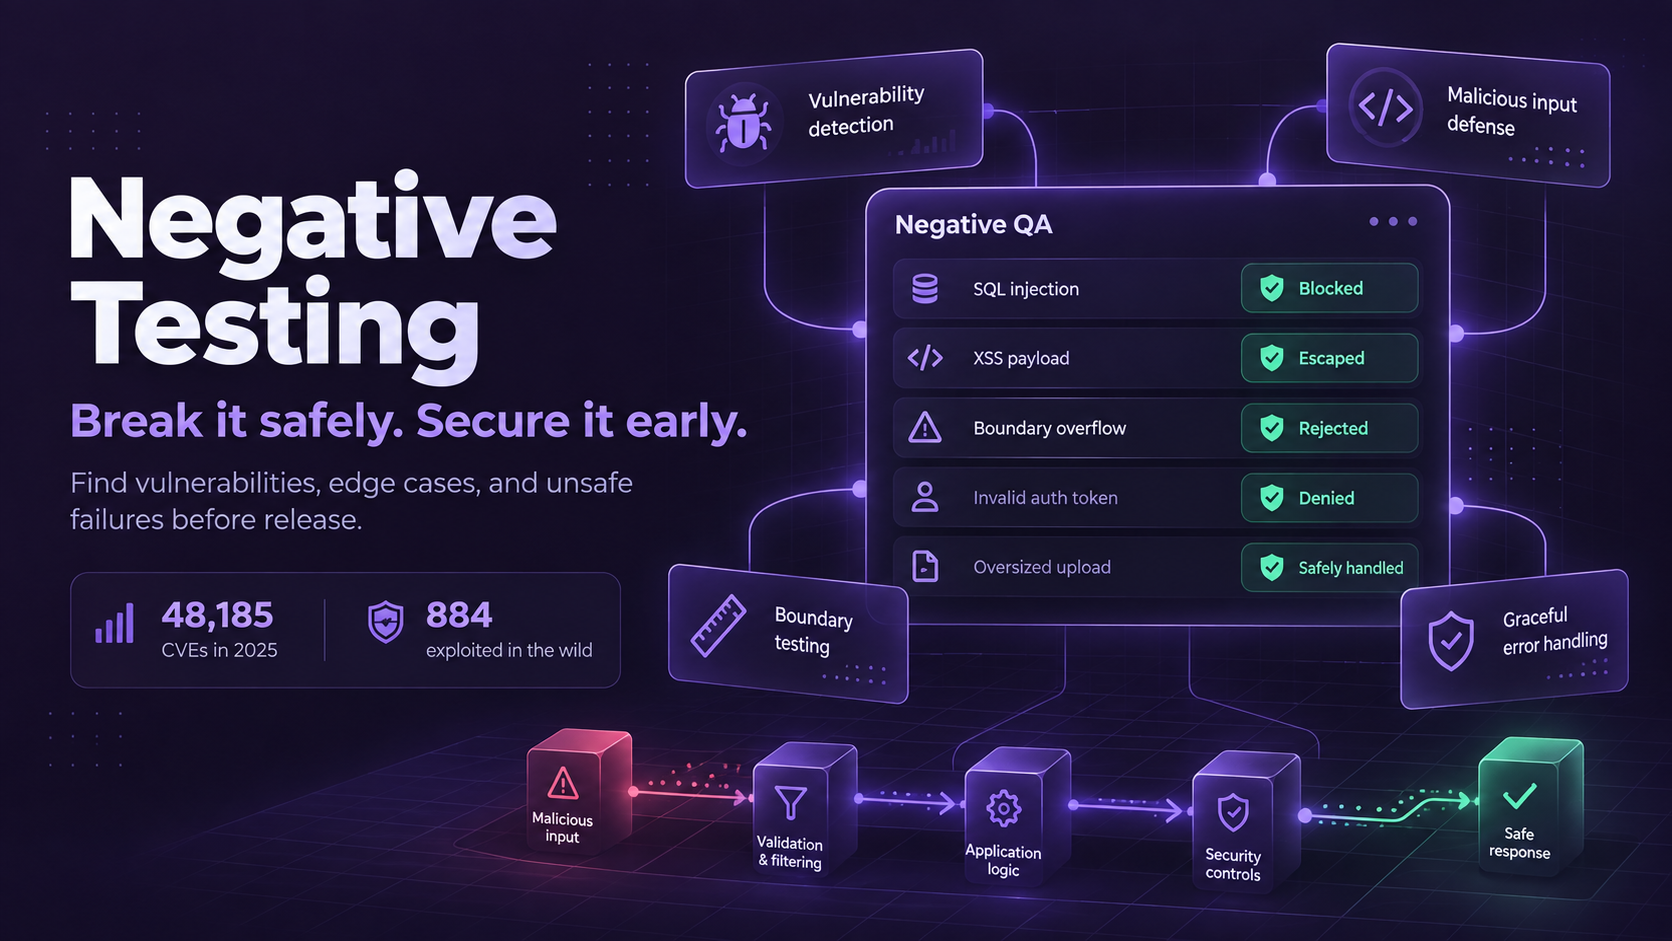
In today's cybersecurity landscape, where 48,185 new vulnerabilities were published in 2025 - averaging roughly 132 new security flaws discovered daily - the traditional approach of only testing what should work is dangerously insufficient. Negative testing in software testing represents a counterintuitive but essential strategy: intentionally trying to break your software to make it unbreakable.
While positive testing confirms that applications work as intended with valid inputs, negative testing in software testing deliberately provides invalid inputs, unexpected conditions, and malicious scenarios to identify potential failure points before cybercriminals do. This proactive approach has become critical as cyber threats evolve and application complexity increases.
Sources: Jerry Gamblin, 2025 CVE Data Review · VulnCheck, State of Exploitation 2026 · MITRE, 2025 CWE Top 25
Negative testing in software testing reveals critical vulnerabilities and edge cases that positive testing cannot detect, preventing costly production failures and security breaches. With 884 CVEs publicly reported as exploited for the first time in 2025 - a 15% increase from 768 in 2024 - organizations cannot afford to skip this essential testing approach.
- What is negative testing in software testing and how does it differ from positive testing?
- Why is negative testing crucial for application security and reliability?
- How do you design effective negative test cases that find real vulnerabilities?
- What are the best practices for implementing negative testing strategies?
- Which tools and frameworks optimize negative testing effectiveness?
What is Negative Testing in Software Testing and How Does It Work?
Negative testing in software testing involves intentionally providing invalid inputs, unexpected data, and boundary conditions to verify that applications handle errors gracefully and maintain stability under adverse conditions. Unlike traditional testing that validates expected functionality, negative testing in software testing challenges applications with scenarios they weren't designed to handle.
This testing approach simulates real-world conditions where users make mistakes, provide incorrect data, or where malicious actors attempt to exploit vulnerabilities. Negative testing in software testing ensures applications respond appropriately to these scenarios rather than crashing, exposing sensitive information, or allowing unauthorized access.
Core Components of Negative Testing
Invalid Input Validation
Testing with wrong data types, formats, and ranges to ensure proper rejection and error handling mechanisms function correctly.
Boundary Condition Testing
Challenging applications with values at the edges of acceptable ranges, including minimum/maximum limits, zero values, and beyond acceptable boundaries.
Security Vulnerability Identification
Simulating malicious input including SQL injection attempts, cross-site scripting attacks, and buffer overflow exploits to identify security weaknesses.
System Stability Testing
Evaluating application behavior under stress conditions, resource constraints, and unexpected system states to ensure graceful degradation.
Error Handling Verification
Confirming that applications provide meaningful error messages, proper logging, and recovery mechanisms when encountering invalid conditions.
How Does Negative Testing Differ from Positive Testing?
Positive and negative testing serve complementary but fundamentally different purposes in comprehensive quality assurance strategies. Understanding this distinction is crucial for implementing effective testing programs.
Focus
Validates that applications work correctly with valid inputs, expected user behaviors, and normal operating conditions. Positive testing confirms that features function as designed when users follow intended workflows.
Approach
Software negative testing deliberately challenges applications with invalid inputs, unexpected user behaviors, and abnormal conditions to identify potential failure points and security vulnerabilities.
Coverage Differences
While positive testing covers expected functionality, negative testing in software testing explores the vast space of everything that could go wrong, providing essential security and reliability assurance.
Risk Mitigation
Positive testing prevents functional defects, while negative testing in software testing prevents security breaches, data corruption, and catastrophic system failures that could result in significant business impact.
Applied to a single login form, the difference looks like this:
| Positive testing | Negative testing | |
|---|---|---|
| Question it answers | PositiveDoes it work when used correctly? | NegativeDoes it fail safely when used incorrectly? |
| Example inputs | PositiveRegistered email and correct password | NegativeWrong password, empty fields, a 5,000-character username, ' OR 1=1 -- |
| Expected result | PositiveUser is logged in and redirected | NegativeLogin is refused with a generic message, the attempt is logged, nothing crashes or leaks |
Why is Negative Testing in Software Testing Essential for Application Security?
The cybersecurity landscape of 2025 demonstrates why negative testing in software testing has evolved from optional to essential. With cross-site scripting (XSS) holding the top spot in MITRE's 2025 CWE Top 25 - and SQL injection right behind it at number two - the need for proactive vulnerability identification has never been more critical.
What Security Risks Does Negative Testing Prevent?
💉 SQL Injection Vulnerabilities
Negative testing in software testing systematically attempts malicious database queries to identify input validation weaknesses that could allow unauthorized data access or manipulation.
SQL injection attacks remain among the most dangerous security vulnerabilities, capable of exposing entire databases to unauthorized access. Software negative testing simulates these attacks in controlled environments to identify vulnerable input points before attackers do.
🧨 Cross-Site Scripting (XSS) Attacks
Given that XSS vulnerabilities topped the 2025 CWE Top 25, negative testing in software testing must include comprehensive script injection testing to identify areas where malicious code could be executed in user browsers.
🧱 Buffer Overflow Exploits
Testing with excessive input data helps identify memory management vulnerabilities that could allow attackers to execute arbitrary code or cause system crashes.
🔑 Authentication and Authorization Bypass
Negative testing in software testing attempts to circumvent security controls using invalid credentials, manipulated session tokens, and privilege escalation techniques.
How Does Negative Testing Improve User Experience?
Beyond security benefits, negative testing in software testing significantly enhances user experience by ensuring applications handle user errors gracefully rather than producing confusing crashes or error messages.
💬 Meaningful Error Communication
Software negative testing verifies that applications provide clear, actionable error messages that help users understand what went wrong and how to correct their input.
🪂 Graceful Degradation
When systems encounter unexpected conditions, negative testing in software testing ensures they degrade gracefully rather than failing catastrophically, maintaining user confidence and system reliability.
🔒 Data Protection
Proper error handling prevents sensitive information from being exposed in error messages or system logs, protecting both user privacy and organizational security.
What Business Costs Does Negative Testing Prevent?
Production failures and security breaches carry significant financial and reputational costs that negative testing in software testing helps prevent through proactive vulnerability identification.
🛡️ Security Breach Prevention
With the average cost of data breaches continuing to rise, negative testing in software testing provides essential protection against vulnerabilities that could lead to costly security incidents.
🤝 Reputation Protection
Security failures and poor error handling can damage customer trust and brand reputation. Software negative testing helps maintain positive user experiences even when things go wrong.
📋 Compliance Assurance
Many regulatory frameworks require evidence of security testing. Negative testing in software testing provides documentation of proactive vulnerability identification efforts.
How To Design Effective Negative Test Cases That Find Real Vulnerabilities?
Creating effective negative testing in software testing requires systematic approaches that target common vulnerability patterns, boundary conditions, and real-world attack scenarios rather than random invalid inputs.
Start With Equivalence Partitioning and Boundary Value Analysis
Two classic test design techniques turn "try some invalid inputs" into a systematic list. Equivalence partitioning splits all possible inputs into groups the system should treat the same way, so one value can stand in for each group. Boundary value analysis then tests the edges of each group, where off-by-one defects tend to cluster.
Take an age field on a sign-up form that accepts whole numbers from 18 to 65:
| Partition | Example values | Expected result |
|---|---|---|
| Valid range | Example values18 40 65 | Expected resultAccepted - these are your positive tests |
| Below range | Example values17 0 -1 | Expected resultRejected with a clear message |
| Above range | Example values66 150 | Expected resultRejected with a clear message |
| Wrong type | Example valuesabc 25.5 18 years | Expected resultRejected - whole numbers only |
| Empty or missing | Example valuesempty string, spaces only, field missing from the request | Expected resultRejected - field is required |
| Malicious | Example values' OR 1=1 -- <script>alert(1)</script> | Expected resultRejected or safely escaped - never executed |
The boundaries themselves get their own tests:
A handful of partitions and four boundary values cover the realistic failure space for this field far better than hundreds of random inputs. The same method scales to every input point in the application.
What Types of Invalid Inputs Should be Tested?
Data Type Violations
Negative testing in software testing should systematically provide incorrect data types - text where numbers are expected, special characters in restricted fields, and non-standard character encodings.
These tests reveal input validation weaknesses that could be exploited by attackers or cause application crashes when users make honest mistakes.
Format Violations
Testing with invalid email formats, malformed URLs, incorrect date formats, and improperly structured data helps identify parsing vulnerabilities and error handling gaps.
Size Extremes
Software negative testing must include empty inputs, excessively long strings, oversized file uploads, and data that exceeds system limits to identify buffer overflow vulnerabilities and resource exhaustion issues.
Character Set Attacks
Unicode exploits, SQL injection attempts, script injections, and command injection payloads should be systematically tested to identify input sanitization weaknesses.
How to Test Error Handling and Recovery Mechanisms?
Negative testing in software testing must verify not just that errors are detected, but that applications handle them appropriately through systematic validation of error responses, logging, and recovery procedures.
Specific Error Message Testing Scenarios:
| Scenario | How to test | ✅ Safe response | ❌ Leaky response |
|---|---|---|---|
| Database Connection Failures | How to testSimulate database outages | ✅ Safe responseGeneric "Service temporarily unavailable" | ❌ Leaky responseExposing connection strings or database schemas |
| File Upload Errors | How to testOversized files (>10MB), invalid formats (.exe instead of .jpg), and corrupted files | ✅ Safe responseClear messages like "File size exceeds 5MB limit" | ❌ Leaky responseRevealing server paths |
| Authentication Failures | How to testFailed login attempts | ✅ Safe response"Invalid username or password" | ❌ Leaky response"Username not found" - enables user enumeration attacks |
Concrete Logging Verification Steps:
Security Event Logging
Trigger failed authentication attempts and verify logs capture IP address, timestamp, and failure reason without recording actual passwords.
Error Correlation Testing
Generate multiple related errors and confirm each receives unique error IDs for tracking while maintaining user privacy.
Log Sanitization
Inject potential XSS payloads in error scenarios and verify logs escape special characters to prevent log injection attacks.
Recovery Mechanism Testing Examples:
⏱ Session Recovery
Force session timeouts during form submission and verify applications either save progress or clearly inform users of data loss.
↩️ Transaction Rollback
Interrupt database transactions mid-process and confirm all changes are properly rolled back without leaving partial data.
🧹 Resource Cleanup
Trigger memory allocation failures and verify applications release resources properly rather than causing memory leaks.
- ✓Applications return to stable state within 30 seconds of error occurrence
- ✓No temporary files or database locks remain after error recovery
- ✓User sessions maintain security context throughout recovery process
What Security-Focused Negative Tests Should Include?
Authentication Bypass Attempts
Negative testing in software testing must systematically attempt to circumvent authentication mechanisms using invalid credentials, session manipulation, and privilege escalation techniques.
Authorization Testing
Verify that users cannot access functionality or data beyond their authorized privileges through URL manipulation, API parameter modification, or session hijacking.
Input Validation Against Malicious Payloads
Software negative testing should include comprehensive testing with known attack patterns including OWASP Top 10 vulnerabilities and emerging threat vectors.
How Do You Implement Negative Testing in Software Testing Successfully?
Effective implementation of negative testing in software testing requires strategic planning, systematic execution, and integration with existing development workflows to maximize security and reliability benefits.
Strategic Planning and Risk Assessment
Risk-Based Prioritization: Focus negative testing in software testing efforts on high-risk areas including user input validation points, authentication mechanisms, authorization controls, and external interface connections.
Applications handling sensitive data, financial transactions, or personal information require more comprehensive software negative testing coverage due to higher potential impact of security failures.
Threat Modeling Integration: Negative testing in software testing should align with threat modeling efforts to ensure testing scenarios reflect realistic attack vectors and business-relevant security concerns.
Essential Implementation Steps
Test Environment Preparation
Negative testing in software testing requires isolated environments with comprehensive monitoring, logging, and rollback capabilities to safely test destructive scenarios without impacting production systems.
Test Case Development
Create systematic software negative testing scenarios that cover input validation, boundary conditions, security vulnerabilities, and error handling across all application components.
Execution Framework
Implement automated execution frameworks that can safely run destructive tests while capturing comprehensive results for analysis and remediation.
Results Analysis
Negative testing in software testing requires careful analysis to distinguish between acceptable error handling and actual vulnerabilities requiring remediation.
Professional QA as a Service solutions provide experienced negative testing in software testing capabilities combined with security expertise to identify vulnerabilities and ensure comprehensive coverage across complex application environments.
They're responsive, well-organized, and proactive in identifying and resolving potential risks early.
Integration with Development Workflows
🔁 Continuous Integration
Software negative testing should be integrated into CI/CD pipelines to ensure new code changes don't introduce security vulnerabilities or break existing error handling mechanisms.
🎓 Developer Training
Development teams need understanding of negative testing in software testing principles to write more secure code and properly implement error handling from the beginning.
🤝 Security Collaboration
Negative testing in software testing efforts should involve security teams to ensure coverage of relevant threat vectors and proper vulnerability classification.
Which Tools and Frameworks Support Negative Testing in Software Testing?
Selecting appropriate tools significantly impacts the effectiveness and efficiency of negative testing in software testing efforts, with different tools serving different aspects of comprehensive negative testing programs.
Security Testing Tools
Web Application Security Scanners
Tools like OWASP ZAP and Burp Suite provide automated negative testing in software testing capabilities for web applications, including vulnerability scanning and penetration testing features.
These tools systematically test for common vulnerabilities including injection attacks, authentication bypasses, and session management flaws.
Fuzzing Tools
AFL++ (the actively maintained fork of American Fuzzy Lop), Peach Fuzzer, and similar tools provide automated software negative testing through systematic generation of invalid inputs to identify parsing vulnerabilities and crash conditions.
API Security Testing
Postman, REST Assured, and specialized API testing tools enable comprehensive negative testing in software testing for API endpoints, including authentication, authorization, and input validation testing.
Automated Testing Frameworks
Test Automation Platforms
Selenium, Cypress, and similar frameworks can be configured for negative testing in software testing through custom test scripts that systematically attempt invalid operations.
Load Testing Tools
JMeter, LoadRunner, and similar platforms provide software negative testing capabilities under stress conditions to identify performance-related vulnerabilities and failure points.
Tool Selection Criteria: choose tools that cover security vulnerabilities, boundary conditions, and error handling, integrate with your CI/CD pipeline, and produce reports developers can act on.
What are the Main Challenges in Negative Testing Implementation?
Understanding common obstacles in negative testing in software testing implementation helps organizations develop realistic expectations and effective mitigation strategies.
Destructive Testing Concerns
Negative testing in software testing can be inherently destructive, requiring careful environment management to prevent unintended system damage or data corruption.
Organizations must implement isolated testing environments with comprehensive backup and recovery procedures to safely conduct software negative testing without production impact.
Resource Requirements
Negative testing in software testing often requires specialized security knowledge, creative thinking about attack vectors, and understanding of vulnerability patterns that may require additional training or expertise.
Infinite Possibility Space
The space of potential invalid inputs and attack scenarios is theoretically infinite, requiring strategic prioritization to focus negative testing in software testing efforts on highest-risk scenarios.
False Positive Management
Software negative testing can generate numerous alerts that require careful analysis to distinguish between actual vulnerabilities and acceptable error conditions.
How Do You Measure the Effectiveness of Negative Testing in Software Testing?
Establishing clear metrics demonstrates the value of negative testing in software testing investments and guides continuous improvement efforts.
Vulnerability Detection Metrics
- Security Vulnerability Prevention: Track the number and severity of security vulnerabilities identified through negative testing in software testing before they reach production environments.
- Error Handling Improvements: Measure enhancements in error handling quality, user experience under error conditions, and system stability improvements.
- Compliance Achievement: Document how software negative testing contributes to regulatory compliance requirements and security certification efforts.
Return on Investment Calculation
- Cost-Benefit Analysis: Calculate ROI by comparing negative testing in software testing investment costs against prevented security breach costs, reduced incident response expenses, and improved user satisfaction.
- Production Incident Reduction: Measure decreases in production security incidents, error-related support tickets, and system failures attributable to comprehensive software negative testing.
Continuous Improvement Indicators
- Coverage Expansion: Track growth in negative testing in software testing coverage across application components, attack vectors, and vulnerability categories over time.
- Team Capability Development: Monitor improvements in team security knowledge, testing effectiveness, and vulnerability identification capabilities.
Why Negative Testing Creates Truly Robust Applications
Negative testing in software testing represents an essential shift from reactive to proactive security and reliability assurance. In an environment where roughly 132 new vulnerabilities are published every day, organizations cannot rely solely on positive testing approaches.
The evidence is clear: with 884 CVEs exploited in the wild for the first time during 2025 alone, applications face constant threats from attackers specifically looking for the edge cases and error conditions that positive testing doesn't cover. Software negative testing provides the proactive defense needed to identify and remediate these vulnerabilities before they impact users or business operations.
The future belongs to development teams that embrace negative testing in software testing as an essential component of modern application development. By intentionally breaking software in controlled environments, organizations build applications that remain unbreakable in production environments where security and reliability directly impact business success.
Find the failure points before attackers do
Our ISTQB-certified QA engineers build negative and security test scenarios into your release process - from input validation and boundary cases to authentication bypass attempts.
About CleverixWe are a Sofia-based software engineering and QA company helping product teams build, test, and maintain complex digital systems, including regulated fintech and iGaming platforms. Our managed QA covers functional, API, performance, and security testing. www.cleverix.com
Frequently Asked Questions
What is negative testing in software testing?
Negative testing deliberately feeds an application invalid inputs, unexpected conditions, and malicious scenarios to confirm it rejects them safely - with clear error messages, no crashes, and no exposed data - instead of only checking that it works with valid inputs.
What is the difference between positive and negative testing?
Positive testing checks that the application works correctly when used as intended. Negative testing checks that it fails safely when used incorrectly or maliciously. You need both: positive tests prevent functional defects, negative tests prevent crashes, data leaks, and security breaches.
What is an example of a negative test case?
Entering 17 into an age field that accepts 18 to 65, or submitting a login form with a wrong password. The expected result is a clear rejection - for the login, a generic "Invalid username or password" message that does not reveal whether the username exists.
Is negative testing the same as security testing?
No, but they overlap. Negative testing covers any invalid or unexpected condition, including honest user mistakes, boundary values, and system failures. Security testing focuses on deliberate attacks. Injection attempts and authentication bypass tests belong to both.
How many negative test cases do you need?
Use equivalence partitioning and boundary value analysis to cover each class of invalid input and each boundary, then prioritize by risk: authentication, payments, and user input points first. The goal is coverage of realistic failure modes, not a large number of tests.